Enterprise AI Adoption in Hong Kong: A 6-Step Roadmap
Which AI pilot should you approve first, who owns it, what will it cost, and when should you scale or stop? A six-step roadmap built on the PCPD Model Framework.
Meowket's take Most useful for Hong Kong commercial leaders moving AI initiatives from experimental pilots into compliant production systems.
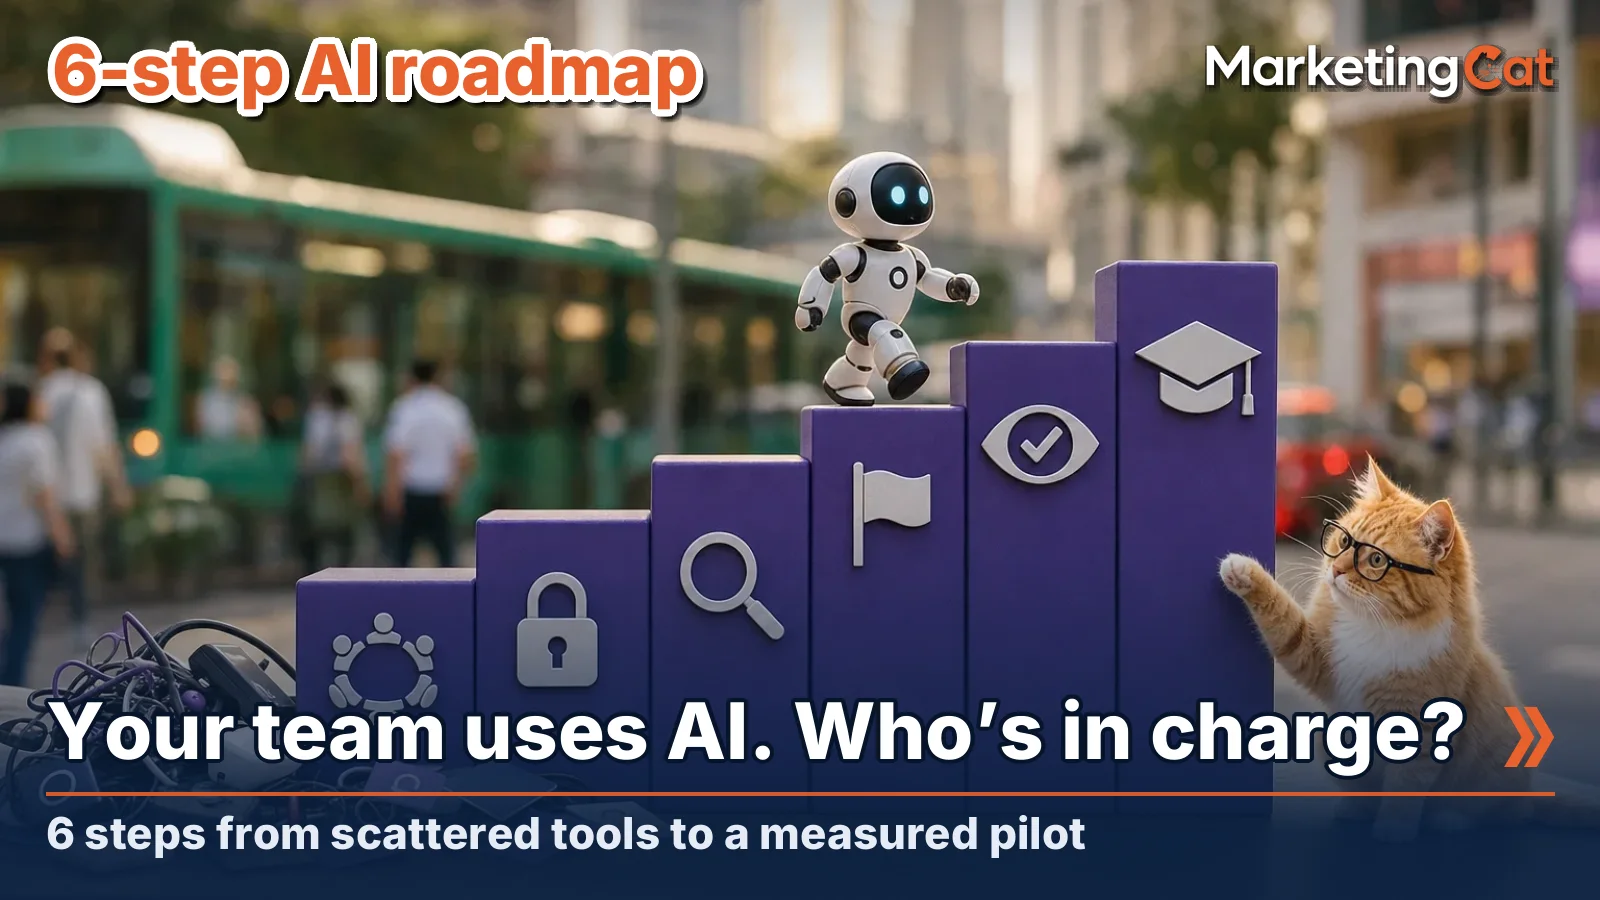
Most Hong Kong companies don’t need help to start using AI. Marketing, sales and operations staff are already using ChatGPT, Copilot or AI agents. What’s usually missing is a shared set of rules: which data can go into which tool, which processes may be automated, who signs off, and how results are measured. This guide turns the Privacy Commissioner’s Artificial Intelligence: Model Personal Data Protection Framework (June 2024), with other official and industry sources, into a six-step roadmap. Each step names an owner and the document or decision it should produce, so you can decide which AI pilot to approve first, what it will take, and when to scale it or stop.
Key Takeaways
- AI is already widespread among the organisations the PCPD checked: in its 2026 compliance check, 57 of 60 (95%) used AI in day-to-day operations, and 29 of those 57 (about 51%) used three or more AI systems. These are inspected organisations, not all Hong Kong businesses.
- Hong Kong has no AI-specific law, but the Personal Data (Privacy) Ordinance applies to AI in full. The PCPD’s Model Framework is guidance, not law, and covers four areas: strategy and governance, risk assessment and human oversight, customisation and management of AI systems, and stakeholder communication.
- MarketingCat’s six-step roadmap gives each step an owner and an output, from an approved AI policy to a scale, revise or stop decision after one measured pilot. Vendor vetting and AI agents need the closest scrutiny.
Where do Hong Kong companies stand on AI adoption?
The PCPD’s 2026 compliance check gives the clearest local picture, but only of the organisations it inspected. According to the PCPD’s May 2026 statement, 57 of the 60 organisations checked (95%) used AI in day-to-day operations. Of those 57, 29 (about 51%) used three or more AI systems, and 24 (about 42%) collected or used personal data through AI systems. Half of the 60 organisations had more than 500 employees, so the sample leans towards larger organisations and does not describe the whole market.
Readiness is a separate question, measured by a different study. Cisco’s 2025 AI Readiness Index surveyed senior IT and business leaders at organisations with 500 or more employees in 30 markets. Only about 2% of the Hong Kong organisations surveyed were “Pacesetters”, the group Cisco rates as fully prepared for AI, as Marketing-Interactive reported. A Legislative Council Secretariat paper from July 2026 cites the same survey and notes that this was the lowest share among the 30 markets. The figure describes larger companies, not Hong Kong SMEs.
Company size matters too. OECD data published in January 2026 show that 20.2% of firms in OECD countries used AI in 2025, with 52.0% of large firms against 17.4% of small firms. Those are OECD averages, not Hong Kong figures.
For budget holders, return on investment is the hardest part to benchmark. None of the sources reviewed for this article gives return-on-investment benchmarks for enterprise AI in Hong Kong. Microsoft’s Cloud Adoption Framework guidance warns that without a clear strategy, “AI investment can become fragmented”, and recommends that the AI strategy itself define how value is measured. You’ll need your own baseline before any pilot starts.

What do Hong Kong law and PCPD guidance actually require?
Hong Kong regulates AI through existing law rather than a dedicated statute. In an August 2024 article, the Privacy Commissioner says the Personal Data (Privacy) Ordinance (PDPO) is “principle-based and technology-neutral”. Data users stay bound by all of its Data Protection Principles (DPPs), whatever technology they use to collect and use personal data. That is the binding layer.
Guidance sits on top of the law. It doesn’t create new legal duties, but it shows what the regulator regards as good practice. The Model Framework applies to organisations that procure, implement and use any type of AI system, including generative AI. The PCPD’s launch statement summarises its recommendations in four areas:
- AI strategy and governance
- Risk assessment and human oversight
- The customisation of AI models and the implementation and management of AI systems
- Communication and engagement with stakeholders
In March 2025 the PCPD added the Checklist on Guidelines for the Use of Generative AI by Employees. It helps organisations write internal policies on permitted tools, what information staff may enter, anonymising personal data and human review of output.
Public-sector rules give private firms a useful benchmark. In February 2026 the Digital Policy Office published an AI adoption guide for government bureaux and departments, according to a Legislative Council reply. It prohibits entering confidential or personal data into external or public AI platforms. It also prohibits generating content that infringes copyright or intellectual property rights. The guide binds government departments, not private companies, but it shows where the government draws its own line.
How to build an enterprise AI adoption strategy: a six-step roadmap
The roadmap below is MarketingCat’s framework, not the PCPD’s own list. It condenses the Model Framework’s four areas and adds commercial steps from other sources. Each step names who owns it and what it should produce, so progress shows up as documents and decisions rather than activity. The PCPD does not prescribe these six outputs; they are our suggestion.

Enterprise AI Adoption Roadmap: Owners and Outputs
- Set the AI policy and name owners An executive-led, cross-disciplinary committee writes down permitted purposes, who approves new use cases and how value will be measured. Output: an approved AI use policy and a named owner for each use case.
- Assess data and privacy risk Before each deployment, assess the volume, sensitivity, security and quality of the data and how much harm an error could do. Output: a privacy impact assessment and a risk level for each use case.
- Vet vendors and integration Check each supplier’s privacy and security obligations, data user and processor roles, cross-border transfers and integration risks before signing. Output: a completed vendor checklist and data processor terms in the contract.
- Pilot one use case, then decide Start with one use case that has a measured baseline and one primary KPI, choosing the option that needs the least operational ownership. Output: a pilot scorecard and a scale, revise or stop decision.
- Set human review by risk Match the level of human oversight to the risk, require human approval for decisions with a significant impact on individuals, and audit periodically. Output: the oversight level, an audit log and an AI incident response plan.
- Train staff and review regularly Train staff on approved tools and AI privacy risks, update team workflows, tell stakeholders how you use AI, and re-run risk assessments when systems or rules change. Output: training records and an updated policy.
The owners below are our suggestion for a mid-sized commercial organisation; smaller firms can combine roles.
| Step | Suggested owner | Output | PCPD Model Framework area |
|---|---|---|---|
| 1. AI policy and owners | Senior sponsor and the AI governance committee | Approved AI use policy; named owner per use case | Area 1: strategy and governance |
| 2. Data and privacy risk | Data protection officer with the business owner | Privacy impact assessment and risk level | Area 2: risk assessment and human oversight |
| 3. Vendors and integration | IT or security, with legal or compliance | Vendor checklist; data processor terms | Areas 1 and 3 |
| 4. One measured pilot | The business owner of the use case | Pilot scorecard; scale, revise or stop decision | Not a Model Framework area (MarketingCat advice) |
| 5. Human review by risk | Business owner, checked by the committee | Oversight level, audit log, AI incident response plan | Areas 2 and 3 |
| 6. Training and reviews | Team leads and HR, with the committee | Training records; updated policy | Areas 1 and 4 |
The PCPD’s 2026 check gives useful benchmarks for steps 1, 2, 5 and 6. They all come from the 24 organisations that collected or used personal data through AI systems. All 24 provided Personal Information Collection Statements. Of the 24, 19 (about 79%) had established AI governance structures, such as an AI governance committee or designated staff; 19 (about 79%) conducted privacy impact assessments before implementation; and 19 (about 79%) used a human-in-the-loop approach. 20 of the 24 (about 83%) provided AI-related training for employees, and of those 20, 18 (90%) included AI privacy risks in the training. These figures describe the organisations inspected, not all Hong Kong businesses, and they are practices, not legal obligations.
Who should sit on the AI governance committee?
The Model Framework recommends an AI governance committee (or similar body) with enough resources, expertise and authority to steer the AI strategy, reporting to the board. The Privacy Commissioner describes a “cross-disciplinary and executive-led AI governance committee” as indispensable. For a commercial team, that usually means a senior sponsor plus marketing, sales, IT or security, legal or compliance, and the data protection officer. Microsoft’s guidance separates roles in a similar way: a central function, such as an AI Center of Excellence, sets organisation-wide policies and boundaries, and business groups pursue opportunities within them. That split lets marketing move quickly without each team writing its own rules.
Which AI use case should you pilot first?
Start with use cases where the value is easy to measure and personal data is minimal or absent. Microsoft’s framework divides AI uses into two groups: improving individual efficiency, such as drafting and research, and automating business functions, such as agents and forecasting. It advises approving the solution that meets the requirement “with the least operational responsibility”, because greater customisation generally requires more specialised skills and greater operational ownership. The PCPD’s risk factors add the other side: the volume, sensitivity and quality of the data involved, and how severe the harm could be if something goes wrong.
The table scores four typical commercial use cases on value, data risk and effort. Illustrative MarketingCat judgements, not audited deployment results.
| Use case | Potential value | Data and privacy risk | Effort | Suggested first step |
|---|---|---|---|---|
| Draft content from public product information | Medium | Low | Low | Pilot first, with editorial review |
| Summarise anonymised market research | Medium | Low, if properly anonymised | Low | Small pilot; check facts against the source |
| Summarise sales calls into the CRM | High | High | Medium | Privacy and access review first; human approval of each summary |
| AI agent that emails prospects on its own | Potentially high | High | High | Separate legal and platform review; a tightly controlled pilot, last |
A use case with low risk and low effort is the natural first pilot, even when its value is only medium: it tests your approval process before personal data is involved. Before putting CRM notes, call transcripts or tickets into any AI tool, take a few precautions. Get internal approval and use only company-approved tools. Limit and anonymise personal data first. Check the vendor’s terms on data retention, model training and access. Keep a person reviewing important outputs.
What will it cost?
The sources reviewed give no Hong Kong price benchmarks for enterprise AI, so build the estimate from your own quotes and time records. Include every cost line, not just the subscription:
- Licences or subscriptions: per-seat plans, usage-based API charges and paid add-ons.
- Set-up and integration: connecting the tool to your CRM, website or data sources, plus any security review.
- Staff time: the pilot team’s hours, and time for the privacy assessment and legal review.
- Training: for the people who use the tool and the people who review its output.
- Ongoing quality and audit: human review of outputs, periodic audits and re-assessments when the system changes.
For custom builds, our guide to the cost of building AI agents covers the costs of AI agents in more detail.
How do you decide whether to scale a pilot?
A pilot only tells you something if success is defined before it starts. Write down four things: the baseline (for example, current hours per task or the current error rate), one primary KPI, the time frame, and the quality and risk conditions the output must meet. Then run it consistently: use the same inputs and prompts, repeat runs for important questions, and keep a record of what was tried.
At the end of the pilot, the owner makes one of three decisions:
- Scale when the KPI beats the baseline over the full period, the quality checks pass and no privacy or security issue is open.
- Revise when the results are mixed: change the prompt, data or process, and run a second, shorter pilot.
- Stop when the KPI doesn’t beat the baseline, when correcting the output takes longer than the time saved, or when a risk can’t be controlled.
Treat any efficiency gain as a hypothesis until real-world data supports it. Our 2026 B2B AI marketing trends piece covers where Hong Kong teams are applying AI.
AI use-case approval worksheet
The Model Framework recommends setting general criteria for submitting an AI solution to the governance committee for review. One practical way to do that is a one-page worksheet that every team completes before a new use case goes to the committee. A MarketingCat template, not a PCPD form.
| Field | What to fill in |
|---|---|
| Use case and owner | What the AI will do, for which team, and the one person accountable |
| Expected value and cost | The problem it solves, the KPI it should move, and the cost lines above |
| Data and systems | The data classes it uses (public, internal, personal, sensitive) and the systems it can access |
| Risk level and approvals | Low, medium or high, and who must approve (committee, data protection officer, legal) |
| Pilot plan | Duration, baseline, primary KPI and quality threshold |
| Human oversight | Human-in-the-loop, human-in-command or human-out-of-the-loop, and who reviews |
| Vendor and contract | Vendor, data processor terms, data location and whether your data trains its models |
| Decision | Go, revise or stop, with the date and the approver |
Vendor checklist: data compliance and integration
In our view, vendor selection is an easy place to take on privacy risk without noticing. The Model Framework recommends building governance into supplier management, including checking whether suppliers follow international technical and governance standards and which data processor agreements to sign. When an organisation shares data with a supplier and instructs it on customising a model, the Commissioner says PDPO issues “should be considered”. These include each party’s responsibilities as data user or data processor, the legality of cross-border transfers and data security. Use these questions in procurement:
- Roles: Is the vendor acting as your data processor, and does the contract cover its retention and security duties? The PCPD recommends contractual or other means for this.
- Training use: Can the vendor use your data to train its models? The PCPD lists function creep, meaning data used beyond its original purpose, as a risk.
- Data location: Where is data stored and processed, and does that involve cross-border transfer?
- Integration: Will the system run on-premises or on a third-party cloud? The Commissioner advises checking the compliance and security implications of either.
- Components: Are third-party plugins and code verified official versions that have passed security review?
- Data subject rights: Can the system support data access and correction requests, and does it keep logs for traceability and audit?
- Language and pricing: Does the tool handle Traditional Chinese and Cantonese well enough for your content, and how are trials, API usage, extra seats and upgrades charged?
- Standards: Which international technical and governance standards does the vendor follow? Whatever the answer, assess your proposed use against the PDPO.
The sources reviewed do not give Hong Kong pricing or contract benchmarks for enterprise AI vendors. They also do not compare Chinese and English language accuracy for specific tools, so test both in a trial with your own content.
Why agentic AI needs a higher bar
The PCPD has addressed agentic AI directly. Its October 2026 presentation describes agentic AI as systems built on foundation models and connected to tools, databases, memory and operating systems. Such systems can perceive, decide and act on multi-step tasks autonomously. The PCPD warns that agents usually run with higher default access rights. Without strict limits, they may reach large amounts of personal data.
The PCPD names further risks. Unreviewed plugins may contain malicious code. Agents may reuse data for new purposes, including training large language models. In multi-agent systems, inaccurate personal data can cascade from one agent to the next. Its mitigations include data minimisation, stating the use of agentic AI in collection statements and privacy policies, setting retention periods, fencing off which systems an agent can access, granting minimum access rights, verifying plugins, and keeping the system traceable and auditable. Its May 2026 statement adds that organisations should download agentic AI only from official channels and take care when installing plugins or skills. It also recommends a human-in-the-loop approach where an agent’s decisions may significantly affect individuals. The graphic below pairs each risk with its control. Our PCPD agentic AI checklist covers this guidance in detail.

Limitations of this roadmap
This article checks the Model Framework’s recommendations against the PCPD’s official summary in its June 2024 launch statement, the Privacy Commissioner’s August 2024 article and a PCPD presentation from October 2026. Read the full Model Framework before you finalise your own policy.
The 2026 compliance-check figures come from 60 inspected organisations, half of them with more than 500 employees, and are not market-wide. Vendor material from Microsoft and Anthropic describes those companies’ own approaches. The owners, outputs, scores and worksheet in this guide are MarketingCat’s suggestions. Nothing here is legal advice. How the PDPO applies depends on your data, your vendors and your circumstances.
In our view, the biggest risk for most Hong Kong commercial teams isn’t moving too slowly. It’s the untracked spread of AI tools that already handle customer data. This week, list every AI tool your marketing and sales staff use. Note which ones touch personal data, and take that list to the person who owns your privacy policy. It’s the raw material for step 1.
Frequently Asked Questions
How long should an enterprise AI pilot run?
There’s no fixed answer in the sources reviewed. Anthropic, an AI vendor, says in its enterprise transformation guide that pilots can be chosen to show value in 30 to 60 days. Stanford’s Digital Economy Lab, in a playbook on 51 enterprise cases, found transformations measured in weeks in some cases and years in others, so the cases don’t add up to one standard timetable. Set the length by how long you need to collect a fair comparison against your baseline.
Can employees use free public chatbots for work tasks?
Only within a written company policy, and preferably not with confidential or personal data. The Digital Policy Office bars government departments from entering such data into external or public AI platforms. That rule doesn’t bind private firms, but it’s a sensible benchmark. The PCPD’s employee checklist suggests specifying permitted tools, permitted devices, the types and amounts of information staff may enter, and how outputs may be stored and used.
What should we do if an AI tool mishandles personal data?
Follow a plan you’ve prepared in advance. The Model Framework recommends an AI Incident Response Plan covering how to define, monitor for, report, contain, investigate and recover from an AI incident. The PCPD’s employee checklist also covers responding to AI incidents and data breaches. For questions on AI and privacy, the PCPD runs an AI Privacy Protection Hotline on 2110 1155, as listed in its October 2026 presentation. Get legal advice on any notification decisions.
Do government AI initiatives help private companies?
Possibly, though the sources don’t show direct support for marketing teams. The 2026-27 Budget proposed an AI+ and Industry Development Strategic Committee to drive industry transformation. It also planned an AI research institute to start operating in the second half of the year. The government reports that Hong Kong’s computing power stood at 5,000 PFLOPS as of July 2026. Watch for programmes that emerge from these plans.